Keeping an identity platform secure isn’t just about good configuration. It also means staying current on vulnerabilities, patches, and security updates that could affect the platform itself.
But there’s a practical challenge: how do IdentityIQ administrators and security teams make sure they don’t miss an important CVE?
Emails can get buried. Security advisories may not reach everyone who needs them and without a simple CVE subscription model that fits every organization’s workflow, teams can find themselves periodically checking multiple sources for updates.
We decided to bring that information directly to where IdentityIQ administrators are already working.
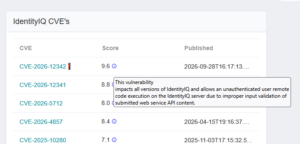
We created a custom SailPoint IdentityIQ widget that gives administrators and security engineers immediate visibility into publicly reported CVEs relevant to IdentityIQ.
The widget queries the NIST National Vulnerability Database (NVD) using its public APIs and displays the results directly within the IdentityIQ home page.
For each vulnerability, administrators can quickly see:
- CVE identifier
- Vulnerability description
- CVSS severity score
- Published date
- Direct link to the CVE details
We also added visual indicators for CVEs published within the past 60 days, making newly published vulnerabilities immediately stand out.
Instead of checking another website or waiting for someone to forward an advisory, administrators can see relevant vulnerability information as part of their normal IdentityIQ experience. For more information about our products and services or to obtain this widget for FREE – contact us!