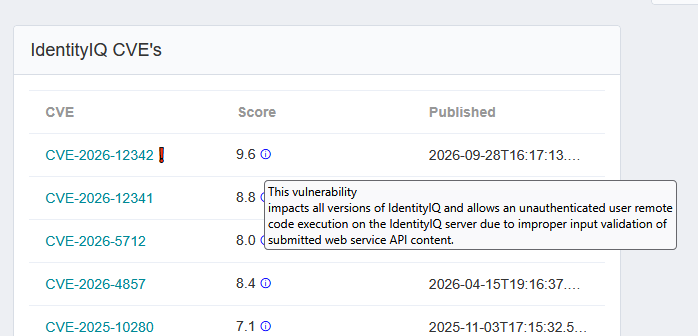
Discover IdentityIQ CVE’s in real-time
Keeping an identity platform secure isn’t just about good configuration. It also means staying current on vulnerabilities, patches, and security
Keeping an identity platform secure isn’t just about good configuration. It also means staying current on vulnerabilities, patches, and security
On September 28, 2026, SailPoint disclosed CVE-2026-12342, a flaw that lets an unauthenticated user run code on the IdentityIQ server. SailPoint rates it 9.6 out of 10, and on October 2 it published e-fix IIQSR-983 to fix it. If you run SailPoint IdentityIQ, you need that e-fix, and you need it ASAP.
There is a strange behavior of OIM 11.1.2.3, which appears to still be present in 12c, that causes unexpected password changes
A majority of organizations implementing Oracle Identity Manager (OIM) struggle with migration and deployment procedures. Migrating a newly developed connector
Weblogic and OIM are vulnerable to Java deserialization attacks over the network. This vulnerability was reported to Oracle in 2015
Organizations in verticals such as Higher Education have requirements around multi-affiliation and multi-valued identity data. In this blog post we